Business Email Compromise (BEC) Security and Consulting Services

Strengthen identities. Detect account takeover. Respond with confidence.

Business email compromise (BEC) is more than a malicious message. Attackers can exploit trusted accounts to impersonate colleagues, redirect payments, and access sensitive information. Avertium helps you reduce that risk by combining stronger identity and email defenses, security validation, and continuous detection and response.

PROTECTION BEYOND THE INBOX

Strengthen your first line of defense

Close gaps in Microsoft 365 and Entra ID configurations, including Conditional Access, phishing-resistant multifactor authentication, application permissions, and mailbox forwarding controls. Turn available security capabilities into practical protections that make accounts harder to compromise.  

  • Microsoft Workshops: Learn how to address identity and email protection, Conditional Access, and safer access practices in your Microsoft environment. Learn about workshops.

  • Microsoft Security Baseline Assessment: Identify identity, email, and access-control configuration gaps and prioritize remediation. Learn about the assessment.

  • Microsoft E5 Configuration and Optimization: Configure and strengthen available Microsoft security capabilities. Learn about E5 optimization. 
Validate Defenses Before Attackers Test Them

Identify exploitable identity weaknesses and test BEC detection logic through targeted assessments and simulated attacks. Understand where controls need improvement and whether suspicious activity produces actionable alerts.

  • Microsoft Adversary Assessment (MAA): Validate that simulated BEC activity produces the expected telemetry, correlated detections, and actionable alerts. Learn about MAA.

  • Social Engineering Assessment: Test susceptibility to phishing and impersonation while evaluating identity controls and security awareness. Learn about Social Engineering Assessment. 

  • Purple Team Engagement: Validate and refine detection and response through collaborative, real-world attack simulations tailored to your environment. Learn about Purple Team. 
Disrupt Compromise Across Your Environment

Get expert investigation, escalation, and authorized response to help limit an attacker’s access. Avertium analysts investigate patterns such as unusual sign-ins, MFA abuse, unexpected mailbox access, and suspicious forwarding rules, then take action to disrupt advancement.

  • Fusion MXDR for Microsoft: Connect Microsoft Defender XDR and Sentinel with 24x7 expert monitoring, investigation, and authorized response to detect and contain BEC across identities, email, and endpoints. Learn about Fusion MXDR for Microsoft.

  • Fusion MXDR for SentinelOne: Combine SentinelOne AI SIEM and XDR with Microsoft 365 identity and email signals, 24x7 expert investigation, and authorized response to identify and disrupt BEC activity. Learn about Fusion MXDR for SentinelOne.
Address Remaining Exposure

Turn security findings into implemented improvements. Our specialists work alongside your team to prioritize and address configuration, access-control, and deployment gaps and apply strategic leadership to improve security posture. 

  • Remediation services: Work with security consultants to implement prioritized fixes, strengthen identity and email configurations, and close security gaps that could enable BEC attempts. Learn about remediation services. 

  • Virtual CISO (vCISO): Get strategic security leadership to prioritize BEC risk reduction, strengthen policies and incident response planning, and align ongoing security improvements with business priorities. Learn about vCISO services.

CONTACT US

AVERTIUM SOLUTIONS FOR MICROSOFT SECURITY

A connected approach to BEC

A connected strategy to BEC defense unifies identity, email, endpoint, and human expertise to identify and disrupt attacks before a compromised account becomes a business-wide threat.

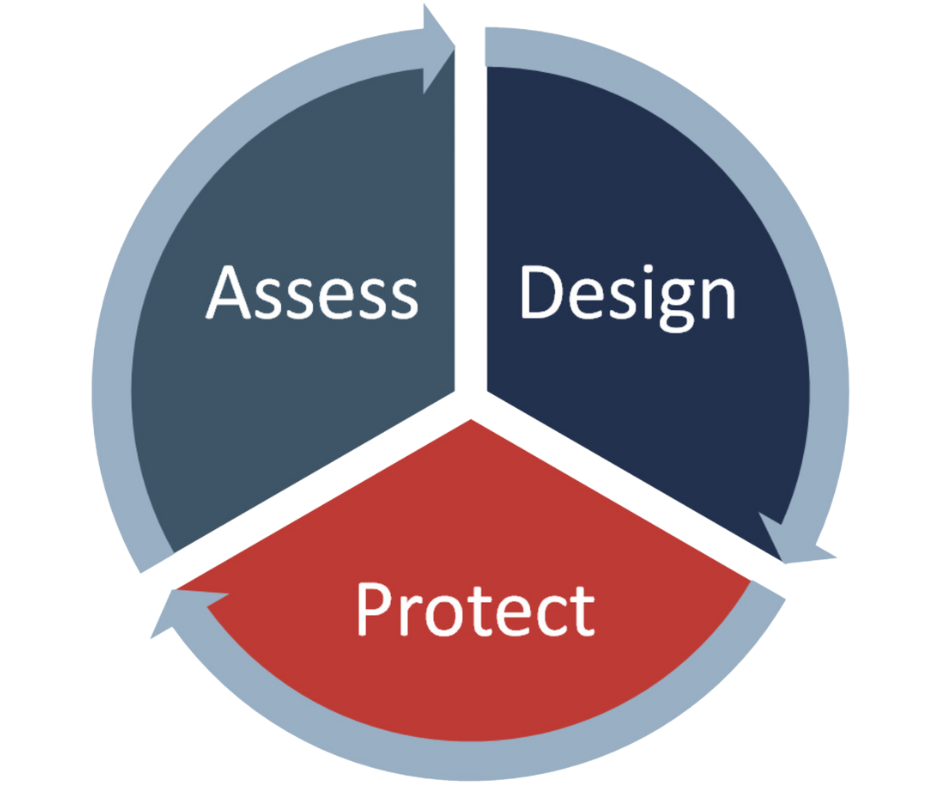
Avertium’s Assess, Design, Protect approach brings assessment, hardening, validation, and managed response together to help reduce the risk of financial loss, data exposure, and business disruption. Your team gains clearer visibility into suspicious activity and expert support to act when it matters.

ASSESS

Identify identity and email security gaps and validate your defenses against BEC scenarios. 

DESIGN

Turn findings into a prioritized roadmap for stronger access controls, secure configurations, and actionable detection and response. 

PROTECT

Put defenses into practice with continuous monitoring, expert investigation, and authorized response through Fusion MXDR.

Build a connected approach to BEC defenses and gain greater bsiness confidence.

 How resilient is your business to BEC? Talk with Avertium about evaluating your identity and email defenses and strengthening your ability to detect and respond to account compromise.


CONTACT US